
NIS2 compliance requirements UK | Guide & Checklist
Contents
What is NIS2?
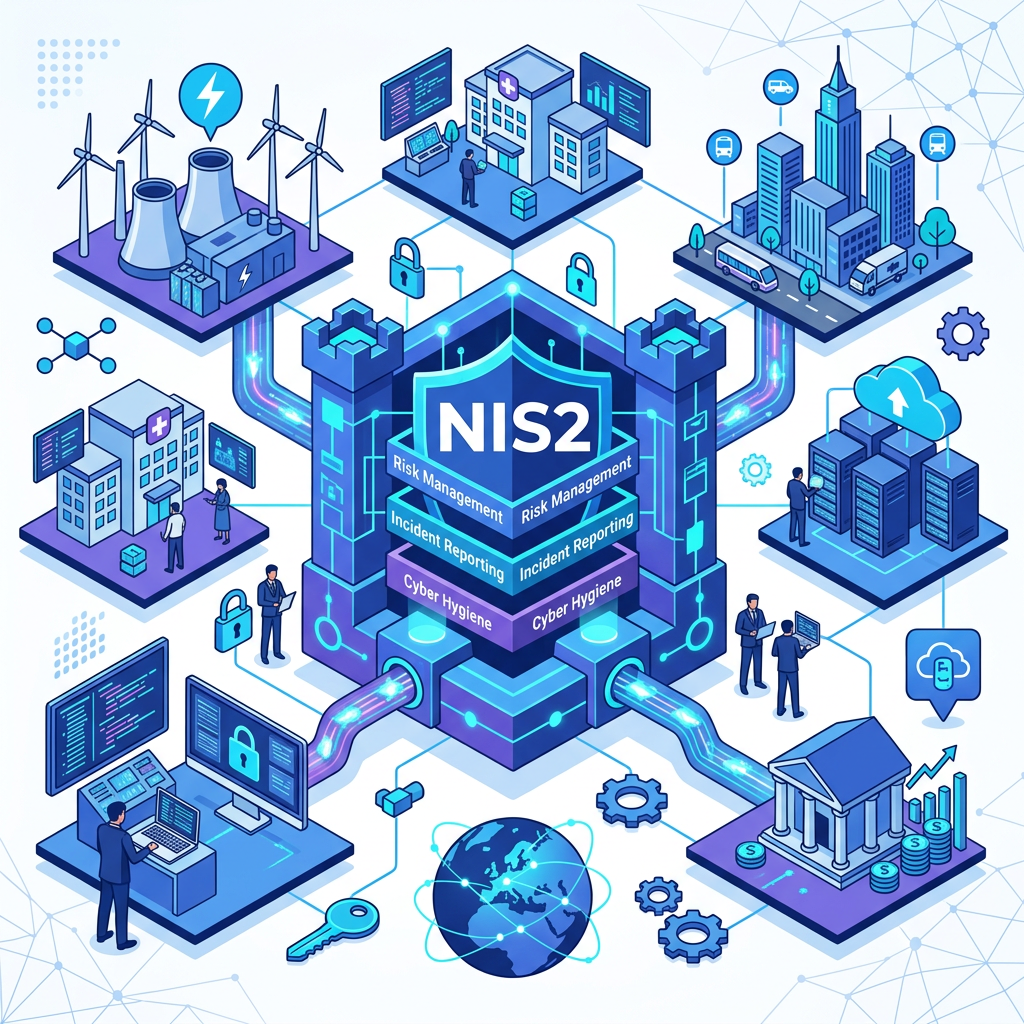
The NIS2 Directive, or the Directive on Security of Network and Information Systems, is an updated legislative framework introduced by the European Union to strengthen cybersecurity across member states. This directive enhances the existing NIS Directive established in 2016, focusing on improving the overall cybersecurity posture and resilience of critical infrastructures and important services within the EU. The directive establishes baseline security requirements and incident reporting obligations for essential and important entities in cybersecurity, which now includes both private and public sector organizations. With cyber threats becoming increasingly sophisticated, NIS2 aims to create a unified approach to cybersecurity across Europe, ensuring that organizations adhere to minimum security practices and effectively manage risks.
Why SMEs Need NIS2 Compliance
SMEs are increasingly becoming targets for cyberattacks due to their perceived vulnerabilities and potential gains for attackers. Compliance with NIS2 is critical for SMEs to mitigate risks associated with data breaches, service disruptions, and reputational damage. A lack of compliance can lead to significant business impacts, including financial losses and legal penalties. According to the Cyber Security Breaches Survey, 39% of UK businesses reported a cyber breach or attack in the past year, underscoring the urgency for SMEs to prioritize cybersecurity. Non-compliance can also have compliance angles, such as GDPR implications, that could affect an SME’s operational capacity. The real-world consequences include loss of client trust and operational downtime, which can severely damage business viability.
Key Risks & Challenges
1. Inadequate Cybersecurity Measures: Many SMEs lack sufficient security protocols. Statistics show that 47% of firms experienced at least one cybersecurity breach last year.
2. Lack of Awareness and Training: Employees often fall for social engineering attacks due to inadequate training. Cybersecurity Awareness training is crucial, as 90% of breaches are caused by human error.
3. Insufficient Incident Response Plans: Without an incident response plan, organizations experience longer recovery times and could face regulatory penalties. The average cost of a data breach in 2022 was $4.35 million.
4. Supply Chain Vulnerabilities: As organizations rely on third-party vendors, they expose themselves to additional risks. In 2021, 61% of organizations reported supply chain attacks.
5. Regulatory Penalties: Non-compliance can lead to fines up to €10 million or 2% of global turnover. All businesses should take NIS2 compliance seriously to avoid these risks.
NIS2 Compliance Checklist
1. Identify your organization's critical services under NIS2.
2. Conduct a risk assessment to identify vulnerabilities in your network security.
3. Implement robust cybersecurity measures, including firewalls and intrusion detection systems.
4. Train employees on cybersecurity best practices and incident response procedures.
5. Create an incident response plan detailing each step to take during a cyber incident.
6. Establish a reporting procedure for incidents that aligns with NIS2's requirements.
7. Monitor and review your cybersecurity practices regularly.
8. Engage with third-party vendors to ensure they also comply with NIS2 standards.
9. Document all compliance efforts and maintain records for audit purposes.
10. Stay informed about updates to NIS2 and adjust your practices as necessary.
Tools & Best Practices
To effectively comply with NIS2 requirements, businesses can leverage various cybersecurity solutions. Consider implementing tools from leading vendors like SentinelOne for endpoint protection that uses AI to detect and respond to threats dynamically. Additionally, Morphisec provides application isolation techniques that prevent attacks from exploiting software vulnerabilities. For email security, Ironscales can help protect against phishing, a common attack vector for many organizations. Adopting these tools enhances your organization’s security posture while facilitating compliance with NIS2 requirements.
Cost & Implementation
Budgeting for NIS2 compliance varies widely depending on the size of the organization and existing security measures. Small SMEs can expect initial costs to range from £5,000 to £15,000, while larger organizations might see budgets start from £20,000 and increase significantly based on complexity. Timeline expectations for full compliance can range from three to six months, depending on the current state of your security practices. Implementation will require resources such as IT personnel, training for staff, and potentially hiring external consultants to ensure that all NIS2 requirements are met adequately.
How to Get Started
Begin your compliance journey by evaluating your organization's current cybersecurity posture. Conduct a comprehensive risk assessment to identify vulnerabilities that need addressing in alignment with NIS2 requirements. Engage your team with training sessions to raise awareness of cybersecurity best practices; avoid common pitfalls like neglecting ongoing monitoring or inadequate documentation of efforts. When in doubt, consider seeking help from cybersecurity experts or consultants, especially regarding complex requirements that may not be within your team's expertise.
Frequently Asked Questions
How long does NIS2 compliance take in the UK?
The timeline for achieving NIS2 compliance can vary significantly based on the maturity of your existing security practices. On average, organizations can expect to take between three to six months to fully comply.
Is NIS2 compliance required for all organizations?
Not all organizations are required to comply with NIS2. Compliance is mainly mandatory for 'essential' and 'important' entities defined under the directive, including sectors like energy, transport, and digital infrastructure.
What frameworks apply in the UK for NIS2 compliance?
In the UK, organizations need to comply with the UK NIS Regulations, which incorporate aspects of the NIS2 Directive alongside the requirements of GDPR to ensure comprehensive data protection.
What should be included in an incident response plan?
An effective incident response plan should include preparation, detection and analysis, containment, eradication, recovery, and post-incident review processes to ensure speed and efficiency during a cybersecurity incident.
Are penalties enforced for non-compliance with NIS2?
Yes, penalties for non-compliance can include substantial fines, which may reach up to €10 million or 2% of the global turnover, as well as reputational damage.
Can smaller businesses afford NIS2 compliance measures?
While the upfront costs can be significant, many smaller businesses can take incremental approaches, using affordable tools and services to enhance their security posture over time.
Ready to strengthen your cyber security posture?
ITR Cyber helps UK organisations select, procure and deploy the right technology.
Published by
ITR Cyber